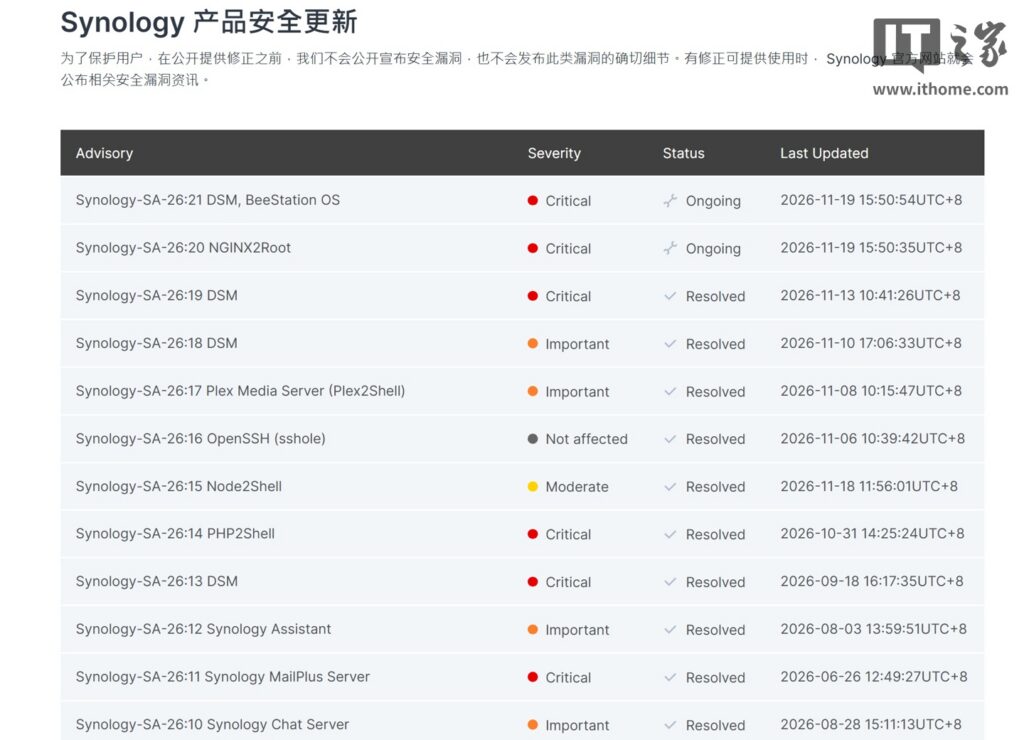
As reported on November 20, 2026, Synology had confirmed a critical vulnerability in the OAuth API used by its DSM operating system. Tracked as CVE-2026-120382, the flaw has a CVSS 3.1 score of 9.8. According to Synology’s security advisory, an attacker could exploit it without authentication or user interaction to remotely read or write arbitrary files on a NAS, or cause a denial of service.
Synology classified the issue as improper handling of command parameter delimiters (CWE-88) and said it involves its OAuth Service package. It had not publicly disclosed exploitation details at the time of the report.
The advisory listed the following status for affected products:
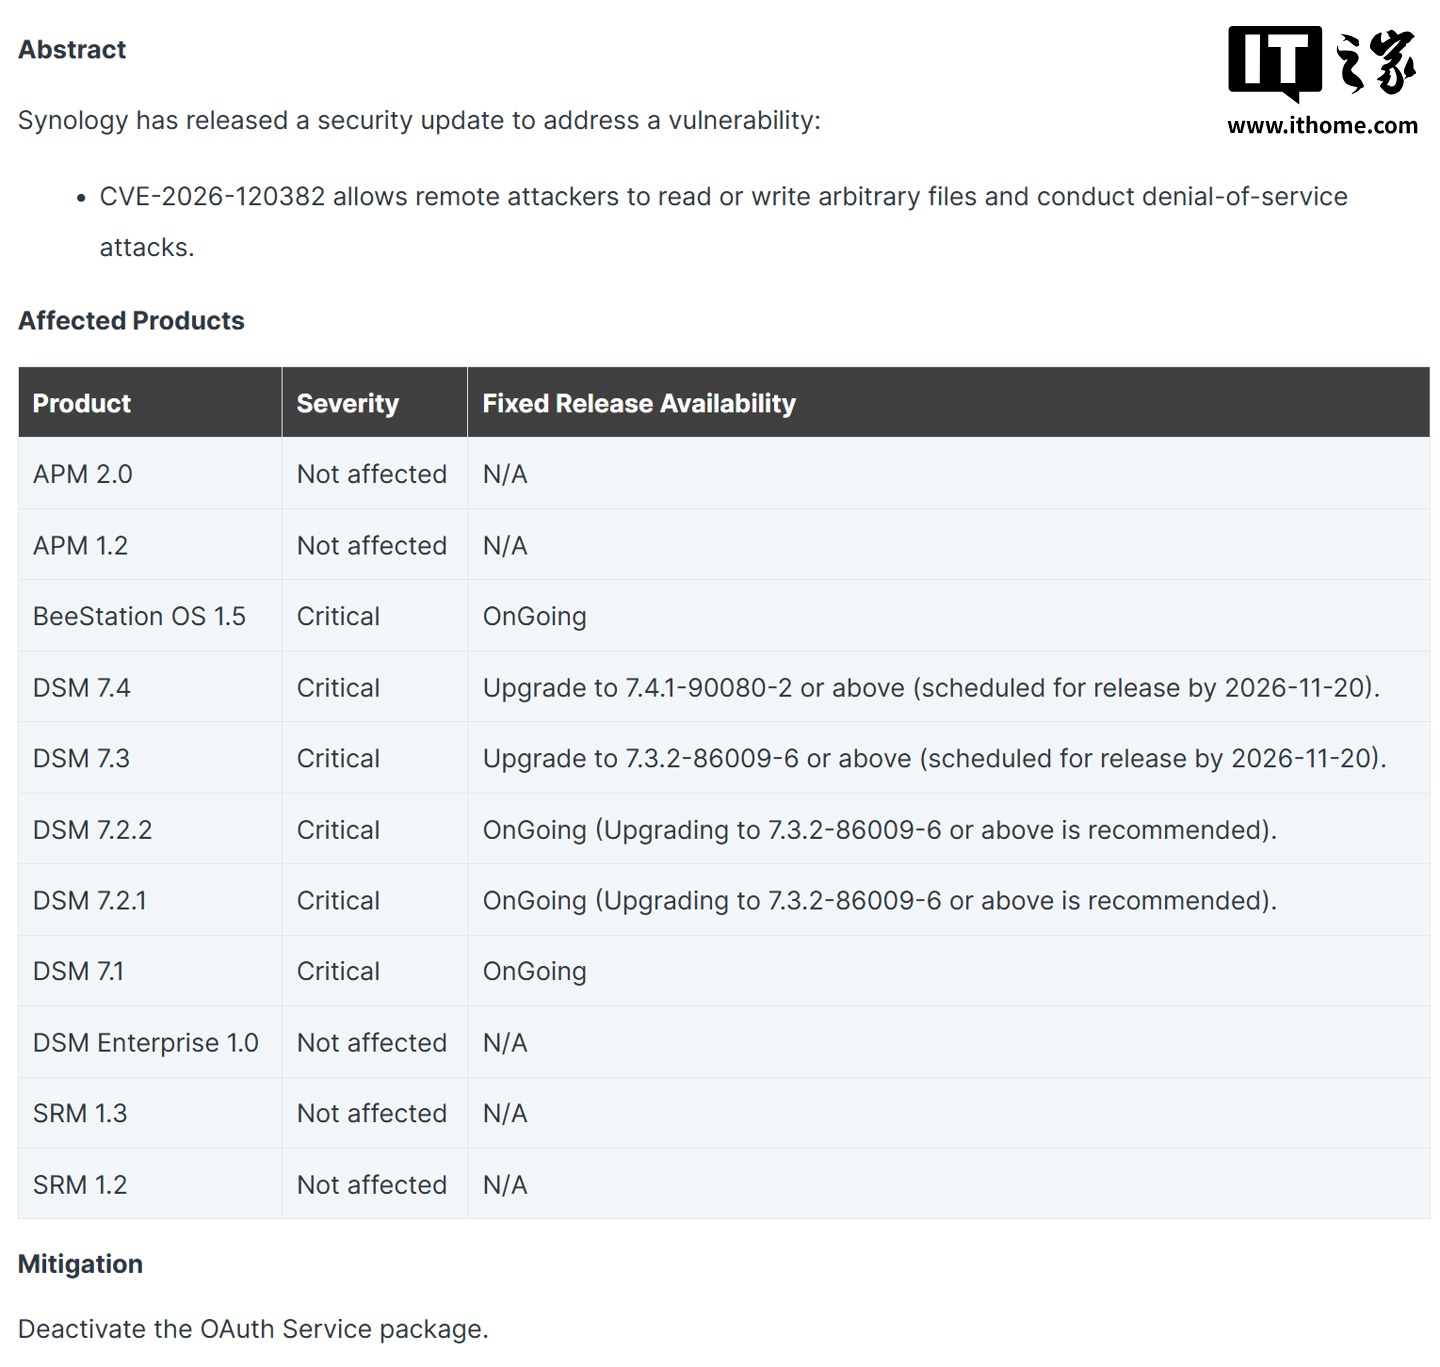
- DSM 7.4: Update to 7.4.1-90080-2 or later. That release was planned for November 20, 2026; the report did not confirm its availability.
- DSM 7.3: Update to 7.3.2-86009-6 or later. That release was also planned for November 20, 2026.
- DSM 7.2.2 and 7.2.1: Fixes were still in progress. Synology advised upgrading to DSM 7.3.2-86009-6 or later.
- DSM 7.1: A fix was still in progress.
- DSM 6.2: Update to 6.2.4-25556-9 or later.
- BeeStation OS 1.5: A fix was still in progress.
Synology listed APM 1.2 and 2.0, DSM Enterprise 1.0, and SRM 1.2 and 1.3 as unaffected. For users unable to update immediately, it recommended disabling OAuth Service in DSM’s Package Center to reduce risk. Doing so may disrupt sign-ins and other services that rely on OAuth authentication, so administrators should check their existing authorization setup before disabling it.